

The silence of a modern security operations center often masks a frantic, invisible war where milliseconds determine the survival of an entire enterprise. In this current year, the luxury of time has become a relic of a slower age, replaced by a relentless environment where machine-speed intrusions bypass human oversight before an alarm can even be acknowledged. The primary challenge lies in the fact that the tools designed to protect digital assets are often built on logic that is simply too slow for the current reality. This transition marks a pivotal moment in the history of cybersecurity, where the fundamental unit of measurement for a breach has shifted from days to seconds. As threat actors harness the power of large-scale automation, the disparity between defensive capabilities and offensive agility creates a widening gap that threatens global stability. Understanding how these processes have been accelerated is the first step in constructing a defense that can actually withstand the pressure of modern digital warfare.
The Death of the Defensive Buffer
The traditional “window of opportunity” for cybersecurity teams is vanishing; what once took a sophisticated threat actor days to execute after an initial breach is now being compressed into mere seconds by autonomous algorithms. As artificial intelligence moves from a buzzword to a tactical engine, the standard cadence of detection and response is being rendered obsolete by the sheer velocity of machine-led intrusion. When an algorithm can scan, exploit, and pivot within a network faster than a notification can reach a human analyst, the buffer that once protected enterprise assets essentially disappears.
This shift necessitates a complete overhaul of how organizations perceive risk and manage their internal perimeters. It is no longer sufficient to have a protocol for when an attack is discovered; the protocol must now focus on preventing the attack from reaching its maximum execution speed. The transition from reactive to proactive defense is not just a strategic choice but a survival requirement in an environment where the adversary operates with the efficiency of a self-optimizing system.
The ErCompressed Breach Timelines
Modern cybersecurity is currently defined by a widening disparity between human reaction times and algorithmic execution speeds. As organizations integrate more cloud services and third-party AI agents, the surface area for potential exploitation expands, creating an interconnected web of risk where a single vulnerability can trigger a cascading enterprise-wide failure. This interconnectedness means that a breach in a remote service can now travel through a supply chain with unprecedented fluidity, often leaving no time for manual intervention.
Furthermore, the reliance on interconnected AI agents introduces a new layer of complexity that traditional firewalls are ill-equipped to handle. If a single automated agent is compromised, it may inadvertently grant the attacker its service-to-service trust levels, allowing for an immediate and deep penetration into the core of a network. This lack of segmentation between automated tools creates a “trust bridge” that modern threat actors are increasingly eager to exploit to bypass legacy security checkpoints.
From Reconnaissance to Exfiltration: The AI-Driven Workflow
Threat actors are utilizing AI to scan source code and binary files at scale, discovering “zero-day” opportunities faster than security researchers can patch them. This automated vulnerability research allows even less-skilled attackers to find entry points that were previously the domain of exclusive nation-state actors. By training models on massive datasets of historical vulnerabilities, these tools can predict where a developer is most likely to have made a mistake, targeting those weaknesses with pinpoint accuracy. Generative AI has revitalized social engineering, causing phishing rates to nearly triple by producing hyper-personalized, error-free lures that bypass traditional email filters and human skepticism. Gone are the days of misspelled emails and awkward phrasing; today’s phishing attempts are indistinguishable from legitimate corporate communications and are often tailored to the specific professional context of the victim. This surge in phishing success rates underscores the terrifying efficiency of AI in manipulating human psychology at a massive scale.
Once inside a network, AI agents can automate credential discovery and lateral movement, inheriting service-to-service trust levels to navigate complex architectures without manual intervention. The shift toward fully autonomous malware allows for bespoke attack campaigns that adapt to defensive maneuvers in real-time, requiring minimal oversight from the human operator. This “agentic” malware can essentially rewrite its own code to evade specific antivirus signatures as it encounters them, ensuring the persistence of the infection.
Geopolitical Friction and Sector-Specific Targeting
According to recent industry data, the government sector accounts for over a quarter of all targeted attacks, driven by a global appetite for intelligence and operational disruption. This sector currently represents 27% of all recorded incidents, making it the most besieged industry globally as state-sponsored actors seek to destabilize rivals. The focus on public institutions suggests that the primary goal of many AI-driven campaigns is not just financial gain, but the erosion of public trust in democratic infrastructure.
The IT and academic sectors remain primary targets due to their wealth of proprietary data and the low tolerance for system downtime in these environments. These sectors serve as the backbone of modern innovation, and compromising them provides a two-fold benefit to the attacker: the theft of intellectual property and the potential for massive supply-chain disruptions. Academic institutions, in particular, often lack the rigorous security frameworks found in the financial sector, making them attractive testing grounds for experimental malware.
While the United States remains a primary focus, attack volumes are intensifying in regions of geopolitical tension, specifically Israel, Ukraine, and Taiwan, where cyber operations serve as a precursor or companion to physical conflict. In these hotspots, digital warfare is a constant reality used to disable infrastructure and spread strategic disinformation. The digital front lines in these regions provide a clear look at how cyber operations have become inseparable from traditional kinetic warfare.
Hardening the Perimeter: Autonomous Threats
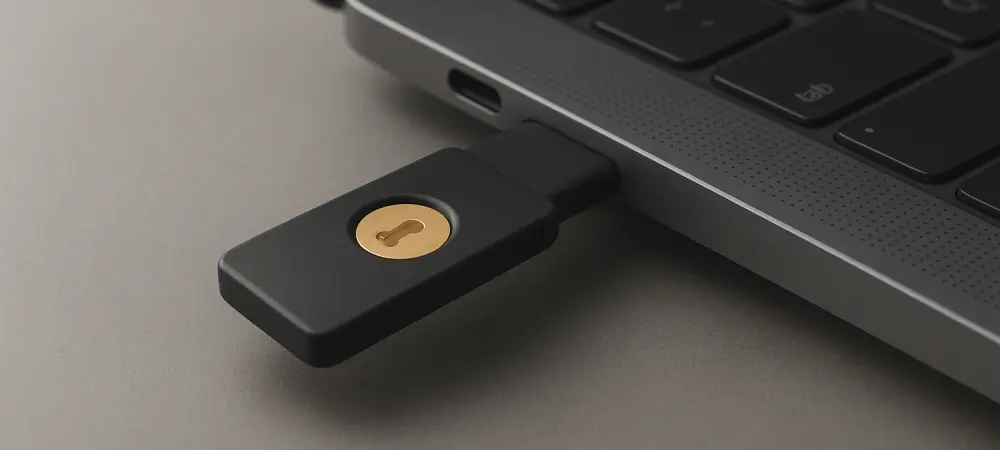
Implementing tiered administration and “Just-In-Time” access models ensured that even if an AI agent was compromised, its reach within the network remained strictly limited. By eliminating standing access, organizations forced attackers to re-authenticate at every critical junction, effectively slowing down an automated attack enough for defensive systems to engage. This zero-trust approach treated every interaction as potentially malicious, which proved vital in containing rapid lateral movement within the network. Moving beyond traditional SMS or app-based codes toward hardware security keys and biometric authentication helped to neutralize the threat of AI-generated social engineering. These phishing-resistant methods removed the human element from the authentication chain, making it significantly harder for a generated lure to succeed. Refocusing on the basics of identity management allowed organizations to close the gaps that AI-driven tools most frequently exploited during the initial stages of a breach. The integration of automated threat intelligence into response frameworks enabled an “active defense” that finally matched the speed of the adversary. This transition toward defensive AI ecosystems became the only viable path to maintain digital stability. IT departments that adopted these high-speed models saw a marked improvement in incident containment. Ultimately, the focus shifted toward building dynamic, self-healing networks that prioritized rapid recovery and automated isolation over the outdated goal of perfect prevention.