

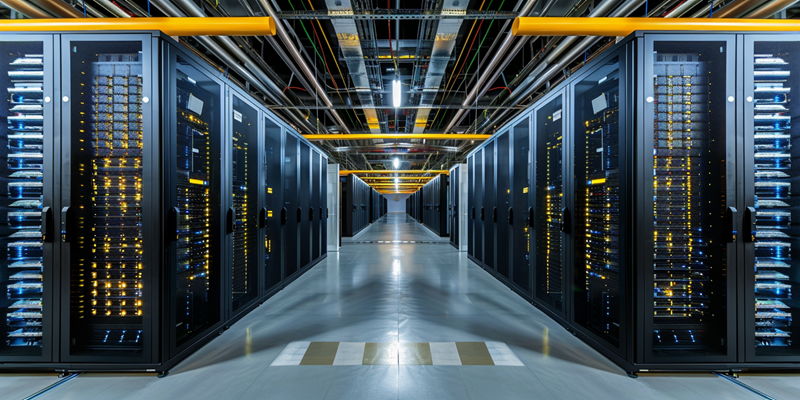
Data centers are digital fortresses, securing valuable assets through various means, such as perimeter defenses and biometric checks. However, despite these measures, server cabinet security often does not receive the attention it should. These cabinets are the final barrier safeguarding each byte of information. Ensuring that they are protected is crucial for the overall security of a data center. Without adequate defense at this level, all other security measures could be rendered ineffective. It is essential to evaluate and reinforce these last-line defenses to ensure that data integrity and confidentiality are maintained. This facet of security should not be overlooked as it can be the deciding factor in the protection of an organization’s critical data. The security of server cabinets must be scrutinized and bolstered to guarantee a truly secure data center.
The Underappreciated Fourth Layer of Data Center Security
Recognized less frequently than its more visible counterparts, cabinet-level security is sometimes the overlooked sentinel in the multilayer security protocol of a data center. The importance of this level of protection is akin to locking the vault inside a fortified bank. While it is critical to guard against external breaches, the internal safeguards serve as the last stand against threats that have managed to penetrate other barriers. This includes protection against malicious insiders—a notorious threat given their potential to cause expansive damage due to their access and knowledge of the data center’s inner workings.
The fourth layer addresses concerns that are unique to the internal workings of a data center. Without secured server cabinets, the data within is vulnerable to unauthorized access by staff or, in the case of co-located data centers, by other customers who share the facility. Physical security measures at this level ensure that each server cabinet is a stronghold in itself, a miniature bastion guarding the critical infrastructure within from insider threats that can elude other forms of security measures.
The Necessity of Advanced Locking Mechanisms and Monitoring
Advanced security for safeguarding critical infrastructure has transcended traditional locks, evolving into high-end systems like biometric and electronic keycard entry for cabinets. Such mechanisms limit physical access to sensitive equipment, paralleling the stringency of digital security protocols, allowing only authorized personnel entry.
To complement these robust locks, vigilant, proactive monitoring is vital. Surveillance cameras and access-tracking software form a preemptive defense against unauthorized interactions with server cabinets, serving both as a deterrent and an alert system for potential security breaches. These measures aren’t stand-alone; they’re integrated into the overall security network of the data center, reinforcing its defensive stance and contributing to an encompassing security solution that protects the facility’s most vulnerable points.
The Practical Challenges of Cabinet-Level Security
Despite its clear benefits, the implementation of cabinet-level security is crowded with practical challenges that need to be addressed. One of the most glaring is the added complexity it brings to the everyday workflow. Technicians accustomed to unencumbered access may find the additional security steps cumbersome, potentially slowing down routine tasks and emergency interventions. Such a system must be designed to be as user-friendly as possible while not compromising on security.
There’s also the issue of managing access permissions, which becomes decidedly more complicated as the granularity of security increases. Each cabinet’s security system needs to be managed and updated with the right access codes, biometrics, and personnel clearances—an administrative burden that requires meticulous oversight. Moreover, the financial cost of upgrading each cabinet with such sophisticated locks and surveillance equipment can be significant, especially for larger data centers. Yet, these investments are critical in an era where data breaches have become both highly sophisticated and costly.
The Imperative for Comprehensive Protection
Traditional security measures are no longer enough for data centers; every potential vulnerability needs to be fortified, including individual server cabinets. Simply put, an unlocked cabinet represents a serious risk to the overall security of a facility. In recognizing the crucial role of cabinet-level security, data center operators can demonstrate their dedication to the comprehensive protection of data.
Investing in cabinet-level security is an essential step toward a robust security strategy and instills confidence in those relying on these services for safeguarding their critical information. When every layer of security is addressed, including the protection at the cabinet level, it not only enhances the reliability of a data center but also showcases a commitment to preserving the integrity of the data stored within. This depth of security is critical to sound digital infrastructure management.