

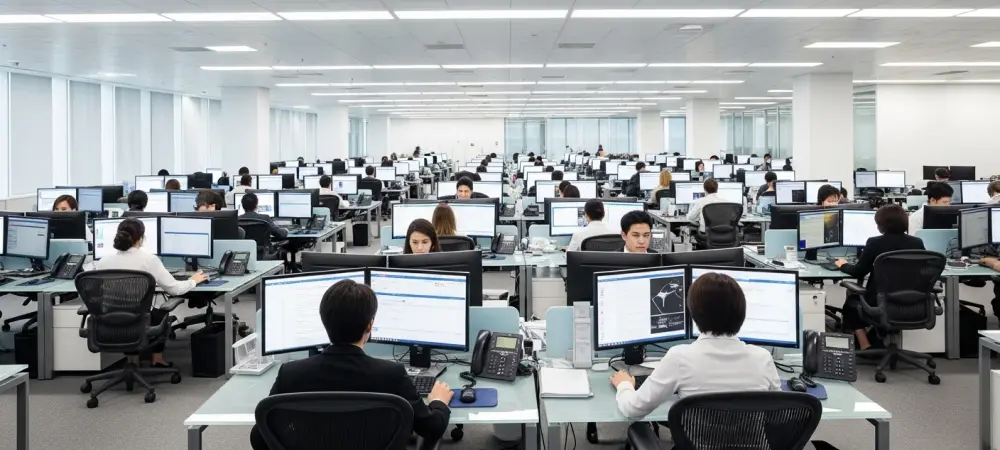
Sophisticated digital criminals have increasingly abandoned traditional back-alley methods in favor of high-tech office environments that resemble legitimate Silicon Valley startups more than shadowy underground syndicates. This paradigm shift was recently brought into sharp focus following a massive coordinated operation led by Europol, which targeted an extensive network of fraudulent call centers based primarily in Albania. The investigation, which spanned several years and involved law enforcement agencies across multiple continents, culminated in a series of high-profile raids that successfully disrupted a criminal enterprise responsible for defrauding victims of approximately $58 million. By treating financial exploitation like a scalable corporate venture, these actors managed to systematically drain the life savings of thousands of individuals. The sheer scale of the operation underscores how modern cybercrime has transitioned into a highly organized, industrial-strength endeavor that requires equally sophisticated international cooperation to dismantle.
The Infrastructure of Industrial-Scale Deception
Corporate Methodology: Running Crime as a Business
The criminal organization in question did not operate as a loose collection of hackers, but rather as a highly structured enterprise employing roughly 450 staff members in a corporate hierarchy. To maintain efficiency and maximize their fraudulent output, the leaders established specialized departments that mirrored those found in any standard multinational firm, including dedicated human resources, information technology, and financial management units. This professionalization allowed the syndicate to scale its operations with terrifying effectiveness, as new recruits were systematically trained to exploit psychological vulnerabilities. The staff was divided into two primary tiers: conversion agents, who were responsible for the initial recruitment and onboarding of potential victims, and retention agents, who posed as expert investment advisors to manage ongoing relationships. These agents utilized localized language skills to build deep rapport with targets across Europe, Canada, and the United Kingdom, ensuring that the deception felt personally tailored and professionally credible.
Technical Exploitation: Utilizing Modern Tools for Theft
Moving beyond simple phishing emails, the network employed a multifaceted approach to gain control over victim assets through a combination of social engineering and advanced technical manipulation. The fraud typically initiated with deceptive advertisements strategically placed on social media platforms and major search engines, promising unrealistic returns on cryptocurrency investments to entice registration. Once a victim engaged, they were often coerced into installing remote access software, which allowed the scammers to take direct control of the victims’ computers under the guise of technical assistance. This level of access not only facilitated the transfer of funds into untraceable cryptocurrency wallets but also allowed the criminals to harvest sensitive personal data for further exploitation. When victims eventually realized they had been defrauded, the organization would often pivot to recovery fraud, masquerading as legal or financial experts who could help recoup the lost funds for a fee, effectively victimizing the same person twice.
Global Implications and Strategic Responses
Regulatory Challenges: The Ongoing Fight Against Cybercrime
The success of this Europol-led mission highlights the critical importance of cross-border police intelligence sharing in an era where digital borders are essentially non-existent for financial criminals. According to recent data from global law enforcement bodies, investment fraud remains the highest-grossing category of cybercrime, frequently outpacing other forms of digital theft due to the high per-victim loss amounts. The Albanian case is not an isolated incident but part of a broader trend involving massive collaborative raids that have recently occurred in major hubs like Dubai and China. These operations demonstrate that while cryptocurrency and remote access tools provide a degree of anonymity, the physical infrastructure required to run large-scale call centers remains a significant point of vulnerability for criminal syndicates. Law enforcement agencies are now prioritizing the seizure of physical assets and the arrest of high-level managers to degrade the operational capacity of these networks rather than just targeting the entry-level staff.
Future Safeguards: Actionable Steps for Digital Resilience
To effectively combat these industrial-scale threats, financial institutions and individual investors had to adopt more rigorous verification protocols and behavioral analysis tools to identify suspicious transaction patterns. Education remains a cornerstone of defense, particularly in recognizing the red flags of unsolicited investment advice and the inherent dangers of granting remote access to personal devices. Authorities recommended that any individual who suspects they have been targeted should immediately contact their local financial regulator and report the incident to specialized cybercrime units to help map the movement of laundered funds. Looking ahead, the integration of real-time monitoring and international blacklists for known fraudulent domains became essential components of a proactive defense strategy. By fostering a culture of skepticism toward high-pressure investment tactics and utilizing multi-factor authentication for all financial interactions, the global community worked toward neutralizing the psychological advantages currently held by organized criminal networks.