

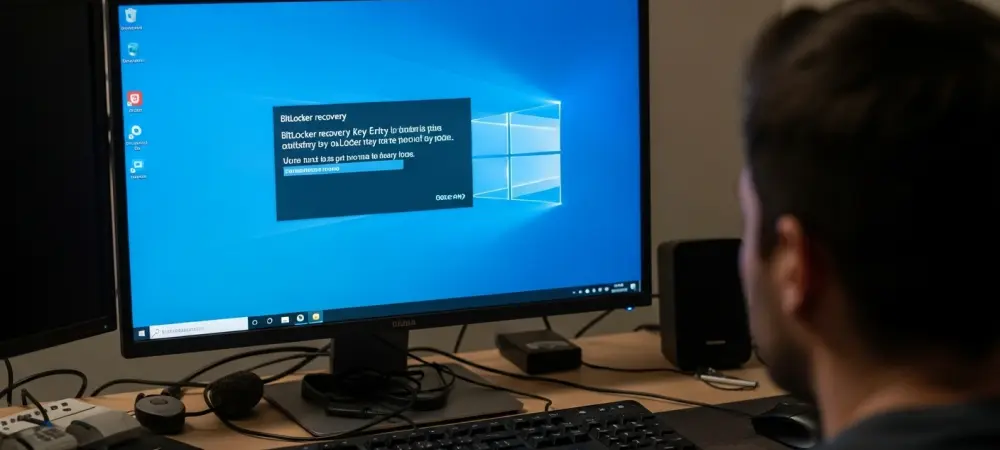
The integration of security patches within the Windows 10 ecosystem remains a complex balancing act between hardening the operating system and ensuring that legitimate users retain seamless access to their encrypted data. When the KB5094127 update was released, reports began to circulate regarding a potential conflict between the installation process and the BitLocker Drive Encryption subsystem, specifically on machines utilizing Trusted Platform Module versions. This phenomenon is not entirely unprecedented, as several previous cumulative updates have occasionally disturbed the integrity of the boot configuration database, leading the system to believe that a tampering event had occurred. For enterprise environments, such a scenario translates into a massive surge in help desk tickets as employees find themselves locked out of their workstations by a blue recovery screen demanding a 48-digit key. Understanding the specific mechanism behind these triggers is essential for maintaining fleet stability.
Security Patch Dynamics: Impact on Encryption Subsystems
The technical intersection of the KB5094127 update and BitLocker often centers on the modification of boot components that the Trusted Platform Module (TPM) monitors for validation purposes. When Windows installs a significant security patch, it occasionally updates the boot loader or other critical startup files that are part of the platform integrity measurements. If the BitLocker protection was not properly suspended prior to the update application, the TPM detects these changes as a deviation from the expected state, subsequently refusing to release the encryption keys. This safeguard is intended to protect against hardware-level attacks, yet it becomes a hindrance when the changes are authorized by the operating system itself. Many administrators observed that devices with specific BIOS configurations were particularly susceptible to this lockout. The resulting recovery prompt serves as a defensive wall, assuming that the boot process has been compromised by unauthorized actors. Beyond the immediate technical failure, the emergence of recovery prompts following the deployment of KB5094127 highlights significant vulnerabilities in organizational disaster recovery planning. In remote work scenarios, where users may not have physical proximity to IT support or their recovery keys, the impact of a locked disk is multiplied, leading to total productivity loss for the duration of the lockout. IT departments managing thousands of endpoints often rely on Microsoft Entra ID or Active Directory for key escrow, but even these solutions can face bottlenecks when a large-scale update failure occurs simultaneously across the fleet. This friction underscores the necessity of rigorous pre-deployment testing in staged environments that mirror the specific hardware profiles used within the company. Failure to account for these variables results in a reactive stance where technicians are forced to manually unlock devices instead of focusing on strategic tasks.
Proactive Management: Strategies for Organizational Stability
Addressing the root causes of BitLocker triggers involves a proactive stance toward update management that prioritizes the suspension of encryption protectors during the installation phase. Modern deployment tools like Microsoft Endpoint Configuration Manager and Intune provide automated scripts that can pause BitLocker for a specific number of reboots, effectively allowing the KB5094127 update to finalize its changes without triggering a security violation. Furthermore, ensuring that the system firmware and BIOS are updated to the latest versions can mitigate many of the compatibility issues that lead to false positives in the TPM validation process. Organizations that consistently verify their recovery key backup status before pushing out cumulative updates find that they can navigate these patches with significantly lower failure rates. By integrating these checks into the standard patching workflow, technical teams ensure that security benefits do not become a liability.
The implementation of a refined deployment strategy effectively neutralized the risks associated with BitLocker recovery events during the rollout of critical system patches. IT professionals adopted a methodology that included mandatory testing on diverse hardware samples before authorizing widespread distribution, ensuring that specific driver conflicts were identified early. They utilized automated verification tools to confirm that recovery keys were successfully synchronized with cloud directories, providing a safety net for users in the field. This systematic approach minimized the volume of support requests and maintained business continuity across various departments. Moving forward, the focus shifted toward implementing more resilient boot protection policies that balanced high security with administrative ease. By treating update deployment as a holistic process rather than a simple file replacement, organizations established a more stable operating environment.