

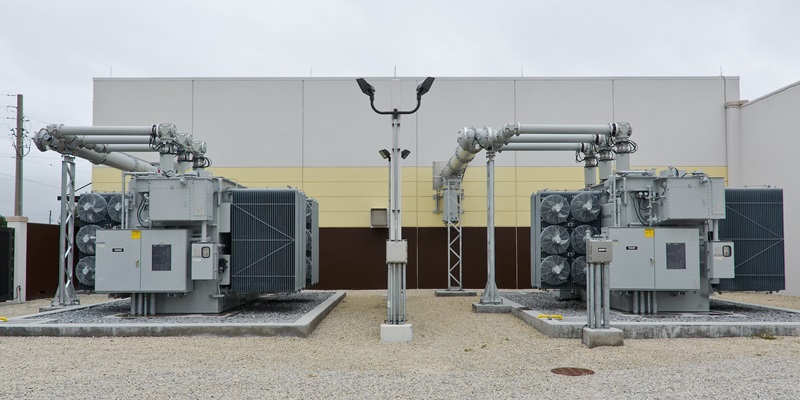
The notorious Russian hackers known as Sandworm recently carried out a targeted attack on an electrical substation in Ukraine, resulting in a brief but impactful power outage in October 2022.
Initial Power Outage and Attack Method
The actor employed sophisticated OT-level LotL techniques to likely trigger the victim’s substation circuit breakers, causing an unplanned power outage. This event coincided with mass missile strikes on critical infrastructure across Ukraine, amplifying the disruption caused.
Second Disruptive Event
Following the initial power outage, Sandworm proceeded to unleash a new variant of CaddyWiper within the victim’s IT environment. This move aimed to cause further disruption and potentially erase any forensic artifacts that could aid in investigations.
Sandworm’s History of Power Grid Attacks in Ukraine
Sandworm has consistently targeted the power grid in Ukraine since 2015, displaying a tenacious and relentless pursuit of disruptive attacks. Notably, they have previously utilized malware such as Industroyer to compromise critical infrastructure.
Intrusion and Initial Access
The intrusion itself is believed to have occurred around June 2022, with Sandworm gaining access to the victim’s operational technology (OT) environment through a hypervisor. This hypervisor hosted a supervisory control and data acquisition (SCADA) management instance for the substation environment.
Execution of the Attack
On October 10, 2022, Sandworm employed an optical disc (ISO) image file to launch striking malware designed explicitly to switch off substations. The result was an unscheduled power outage that had a significant impact on the Ukrainian electrical infrastructure.
Deployment of CaddyWiper
Within two days of the OT event, Sandworm introduced a new variant of CaddyWiper into the victims’ IT environment. This malicious software aimed to perpetuate disruption, possibly removing evidence and hindering forensic investigations.
CaddyWiper and Its Background
CaddyWiper refers to a malevolent piece of data-wiping malware that emerged in connection with the Russo-Ukrainian war in March 2022. It has been linked to several cyber-espionage activities and disruptive attacks on critical infrastructure.
Coordination with Missile Strikes
The eventual execution of the Sandworm attack was timed to coincide with the start of multi-day coordinated missile strikes on critical infrastructure across several Ukrainian cities. The victim’s substation was located in one of these targeted areas.
Immediate Threat to MicroSCADA Supervisory Control System
This attack represents an immediate and significant threat to Ukrainian critical infrastructure environments that rely on the MicroSCADA supervisory control system. The breach exposes the risks associated with dependence on interconnected systems that are vulnerable to cyber intrusions.
Recapping the Sandworm attack on the electrical substation in Ukraine, it becomes apparent that the hackers’ persistence and evolving techniques pose grave risks to cybersecurity and critical infrastructure worldwide. The need for enhanced cybersecurity measures, continuous monitoring, and collaboration among nations has never been more crucial in countering these persistent threats.