

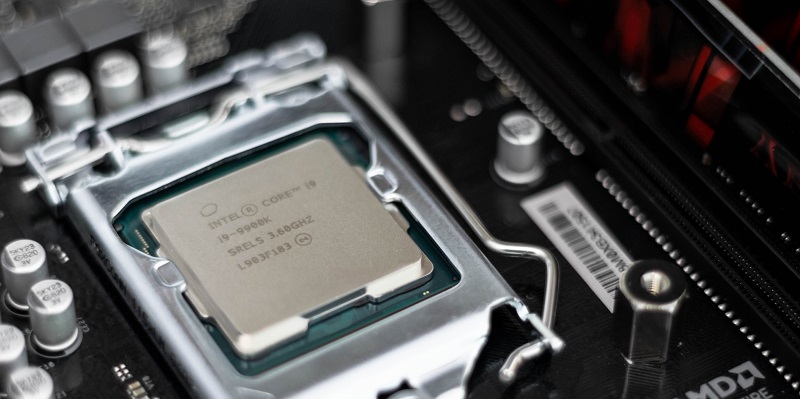
A newly revealed flaw has sent shockwaves through the computer industry, affecting a substantial portion of the world’s computers. This flaw, known as ‘Downfall,’ has a significant impact on all devices running Intel processors manufactured between 2014 and 2021. With Intel controlling a majority of the global market share for CPUs, it is estimated that between 1.5 and 2 billion devices have been affected. To add to the concern, another flaw called ‘Zenbleed’ has been discovered, targeting processors developed by Intel’s main competitor, AMD. The implications of these vulnerabilities are extensive and raise substantial concerns about data security and privacy.
Downfall: Affecting Intel processors
The Downfall vulnerability primarily targets devices powered by Intel processors between the years 2014 and 2021. This includes a wide range of devices such as personal computers, laptops, and servers. The flaw allows for unauthorized access to sensitive data stored within the register, which can potentially lead to data breaches and security breaches. Considering Intel’s dominant market position, a large number of devices worldwide are vulnerable to this flaw. The potential damage could be significant as it extends to Intel’s extensive market reach and the widespread use of their processors.
Zenbleed: A Similar Finding
Mirroring the discovery of Meltdown, a Google researcher has uncovered another flaw named Zenbleed in processors developed by Intel’s main competitor, AMD. Zenbleed exploits a similar vulnerability, potentially allowing unauthorized access to sensitive data. The existence of Zenbleed further underscores the need for hardware manufacturers to prioritize robust security measures to protect user data and privacy.
The Discovery of Downfall
The meticulous work of researcher Moghimi led to the discovery of Downfall. Moghimi uncovered the flaw by examining the ‘gather’ instruction, which is a fundamental operation in Intel processors. Through this investigation, he realized that he could leverage this instruction to gain access to data stored in the register assigned to a different user or application. The implications of this discovery are grave, as it violates the fundamental principles of data isolation and protection. This flaw has far-reaching consequences, enabling attackers to potentially extract sensitive information under the guise of legitimate operations.
Potential attacks and implications
The discovery of Downfall and Zenbleed raises various concerns about data security and the overall integrity of computer systems. With unauthorized access to sensitive data, attackers could initiate a plethora of malicious activities, including identity theft, espionage, and corporate sabotage. The potential for widespread exploitation of these vulnerabilities is a grave concern, requiring immediate attention and action from hardware manufacturers and software developers.
Fixing “Downfall.”
Upon discovering Downfall, Moghimi promptly disclosed the flaw to Intel in August of last year. Since then, Intel has been diligently working on developing a fix for the vulnerability. However, Moghimi contends that the proposed fix is more of a treatment for the underlying problem rather than a complete cure. The fix addresses the immediate issue but does not fundamentally address the lack of isolation within the hardware architecture, leaving room for similar flaws to emerge in the future.
Limitations of the fix
Moghimi emphasizes the importance of better isolation within hardware to mitigate the risk of future vulnerabilities like Downfall and Zenbleed. He argues that unless hardware manufacturers adopt a proactive approach that prioritizes robust security measures, more stories like Downfall and Zenbleed are bound to emerge. The risk of compromising sensitive data through similar architectural vulnerabilities remains a significant concern in an increasingly data-driven world.
The revelations of Downfall and Zenbleed have brought to light the alarming vulnerability of billions of devices running Intel and AMD processors. These flaws highlight the urgent need for improved security measures within hardware architectures, ensuring better isolation of data and protection against unauthorized access. As technology continues to advance, safeguarding data privacy and preventing security breaches must be a top priority for hardware manufacturers, software developers, and industry regulators alike. Only through a collaborative effort can we address the existing vulnerabilities and build a more resilient and secure digital ecosystem for future generations.