

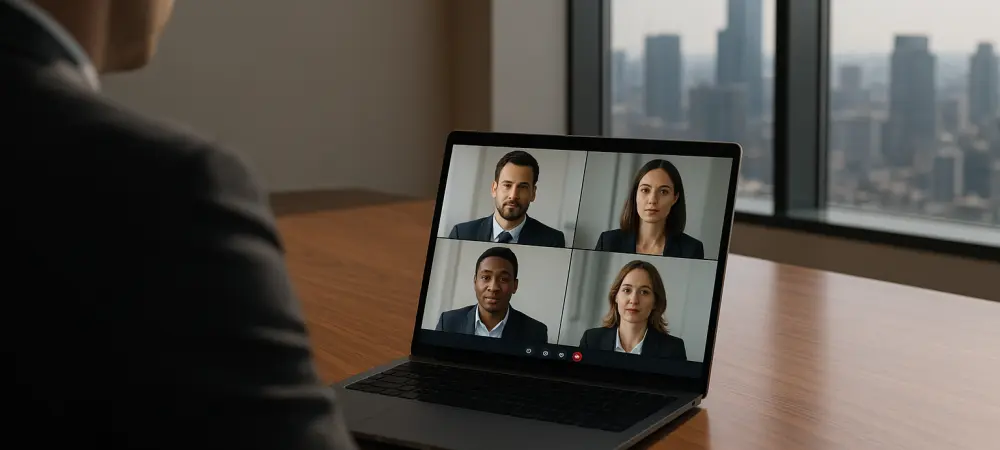
A finance employee at the firm Arup was recently deceived into transferring $25 million after participating in a video call where every colleague was an AI-generated deepfake. This sophisticated heist is not an isolated anomaly but a signal of a broader structural shift in the global security landscape, where generative artificial intelligence acts as both a robust shield and a sharp, unpredictable sword. As the digital environment moves deeper into this automated era, the speed of engagement has accelerated to a point where traditional human-led defenses are struggling to maintain pace. Organizations are finding themselves in a high-stakes environment characterized by a “dual-use” paradox, where the same large language models used to protect critical infrastructure are being repurposed by adversaries to dismantle it. The strategic burden of this transition remains uneven, as the asymmetric nature of cybersecurity continues to favor the aggressor. While defenders must maintain a perfect success rate across millions of daily interactions, an attacker only needs one successful breach or a single exploited vulnerability to achieve their objectives. This dynamic is forcing a fundamental reassessment of digital trust and operational resilience across every sector of the economy.
Strengthening the Defensive Perimeter
Maximizing Protection: Automation and Junior Analyst Support
For modern security operations centers, the sheer volume of telemetry data produced by enterprise networks has long been a primary obstacle to effective threat detection. Generative AI is now fundamentally changing this dynamic by serving as a high-speed interpreter of raw technical logs. By ingesting massive streams of data from across a company’s digital footprint, these models can synthesize complex anomalies into concise, plain-language summaries that are immediately actionable for human teams. This capability allows junior security analysts, who may lack the decades of deep technical training traditionally required to spot subtle signs of lateral movement or privilege escalation, to perform at the level of senior threat hunters. Instead of manually correlating thousands of disparate IP addresses and timestamps, these professionals can now interact with their security stacks using natural language queries. This streamlined workflow has drastically reduced the time required to triage potential threats, ensuring that anomalous behavior is identified and contained before it can escalate into a full-scale data breach.
The integration of these intelligent systems also provides a significant economic advantage by lowering the overall cost of incident response. Statistics from the current year show that organizations utilizing AI-driven triage and containment protocols have saved an average of several million dollars per incident compared to those relying on manual methods. By automating the most repetitive and time-consuming aspects of the investigative process, generative models free up senior human experts to focus on the most complex and strategically significant threats. This collaborative approach creates a force-multiplier effect, where the defensive perimeter is not just reinforced by better code, but by more efficient human decision-making. Furthermore, the ability of these models to provide real-time explanations of why a certain event was flagged as suspicious helps to bridge the skills gap within the industry. As we progress through the current cycle toward 2028, the continuous refinement of these defensive assistants will likely become the standard baseline for any organization serious about maintaining a robust security posture.
Simulation Strategies: Utilizing Synthetic Data for Proactive Defense
Beyond the immediate requirements of real-time monitoring, security teams are increasingly using generative AI to create synthetic datasets for advanced training and system hardening. Modern defense relies on the ability to anticipate and prepare for attack vectors that have not yet occurred in the real world, and generative models provide a controlled laboratory for this experimentation. By utilizing specialized neural networks to generate massive volumes of realistic but artificial network traffic, defenders can battle-test their infrastructure against a wide variety of sophisticated tactics, such as advanced password-cracking or low-and-slow data exfiltration attempts. This proactive approach allows organizations to identify hidden weaknesses in their architecture without risking the integrity of their live production environments. These simulations are particularly effective at uncovering “blind spots” in existing security tools, providing a rigorous stress test that reflects the complexity of the modern threat environment while ensuring that no actual sensitive data is ever exposed during the process.
This shift toward predictive security is further enhanced by the creation of highly realistic attack scenarios that help refine the coordination of human response teams. By simulating the precise characteristics of a state-sponsored espionage campaign or a complex ransomware attack, organizations can run high-fidelity “war games” that accurately mirror the psychological and technical pressures of a genuine crisis. These exercises ensure that the communication protocols and decision-making frameworks used by leadership are resilient enough to withstand the chaos of a high-speed digital assault. The insights gained from these simulations are then used to fine-tune the automated detection models, creating a virtuous cycle of continuous improvement. As these synthetic training environments become more sophisticated, they allow for the development of “immune system” architectures that are naturally resistant to the types of adversarial patterns identified during simulation. This strategic resilience ensures that defensive mechanisms remain agile and capable of adapting to the rapid evolution of malicious techniques.
The Evolution of Malicious Exploitation
Malicious Agility: Scaling Deceptive Tactics and Social Engineering
The rapid democratization of generative tools has provided cybercriminals with a level of agility that was previously reserved for the most advanced state-sponsored actors. Perhaps the most visible impact is the total transformation of social engineering and phishing attacks. The era of the obvious, poorly written email is effectively over, replaced by perfectly crafted messages that mimic the unique voice, tone, and professional jargon of a target organization. Because AI models can generate these communications at scale without the traditional red flags of grammatical errors or awkward phrasing, the success rate of these deceptive campaigns has climbed significantly. This makes the human element of security more vulnerable than ever before, as even the most well-trained employees struggle to distinguish between a legitimate internal request and a malicious fabrication. The ability of attackers to automate the research phase of these campaigns by scraping public data to create highly personalized lures has turned social engineering into a precision weapon.
Simultaneously, the technical barrier for developing and deploying malicious code has dropped to an unprecedented low. Threat actors are now leveraging coding assistants to write, debug, and obfuscate malware in real-time, effectively turning helpful productivity tools into active weapons. This allows for the creation of polymorphic code that can change its signature each time it is deployed, making it nearly impossible for traditional antivirus software to detect. Criminals are also using these models to break down complex malicious objectives into small, innocent-looking sub-tasks that can bypass standard security filters and safety guardrails. This structural shift means that even a single individual with limited coding knowledge can now launch sophisticated, multi-stage attacks that target specific enterprise vulnerabilities. The result is a landscape where the frequency and complexity of digital assaults are increasing exponentially, outstripping the capacity of many standard defensive frameworks and necessitating a fundamental change in how software integrity is verified.
Institutional Risk: The Impact of Deepfakes on Trust
The rise of hyper-realistic deepfakes represents a catastrophic erosion of the foundational trust that underpins modern institutional operations. As demonstrated by the recent multi-million dollar losses at firms like Arup, the ability to clone the voices and faces of executives during live video calls has rendered visual and auditory confirmation obsolete as a method of identity verification. This technology has moved beyond simple novelty and into the realm of high-stakes financial and corporate espionage, where the goal is to trick employees into bypassing established safety protocols. When a worker believes they are receiving direct orders from their CEO in a live, interactive environment, their natural instinct is to comply, making this one of the most effective methods for facilitating unauthorized fund transfers or the theft of intellectual property. The psychological impact of these attacks is profound, as it creates an environment of pervasive skepticism where no digital communication can be taken at face value.
The consequences of this erosion of trust extend far beyond immediate financial losses, impacting the very nature of corporate governance and communication. Organizations are finding that their existing identity and access management systems are insufficient to counter the persuasive power of AI-generated content. This has led to a renewed focus on out-of-band verification and the implementation of more rigorous internal controls that do not rely solely on human intuition. The challenge for the period from 2026 to 2028 will be to develop new verification standards that can withstand the increasing sophistication of generative models. This includes the widespread adoption of cryptographically secure identity markers and the use of multi-person authorization for any significant strategic or financial action. Without these safeguards, the digital economy remains highly susceptible to a new breed of fraud that leverages the human brain’s inherent trust in visual and auditory signals to achieve its destructive ends.
Navigating the High-Speed Digital Frontier
Autonomous Warfare: Adversarial Trends and Strategic Resilience
We have entered a period defined by the rise of autonomous cyber warfare, where the majority of an infiltration can be conducted by specialized AI agents with minimal human oversight. These agents are capable of scanning for vulnerabilities, exploiting them, and moving laterally across a network at speeds that are incomprehensible to human defenders. Recent data indicates that some AI-enabled operations can achieve a total system compromise in less than thirty seconds, leaving virtually no window for manual intervention. This velocity makes traditional “detect and respond” models obsolete, as the damage is often done before an initial alert can even be processed by a human analyst. To counter this, defenders are being forced to deploy their own autonomous agents to conduct real-time battle for control of network infrastructure. This machine-on-machine conflict represents a major escalation in the digital arms race, where the side with the most efficient and adaptable algorithms holds the decisive advantage.
To survive in this high-speed environment, organizations must move beyond static, perimeter-based defenses and adopt a philosophy of strategic resilience. This involves a comprehensive monitoring of the entire AI supply chain, ensuring that the models being used for internal operations have not been compromised by data poisoning or adversarial inputs. Resilience also means assuming that a breach will eventually occur and focusing on the ability to isolate and neutralize threats automatically before they can reach the core of the network. This “zero-trust” approach requires continuous verification of every user and device, combined with the use of AI to detect subtle deviations from normal behavior that might indicate an autonomous agent is at work. By prioritizing the visibility of internal systems and the speed of automated response, businesses can better prepare themselves for a world where the primary actors on the digital battlefield are no longer humans, but highly intelligent, self-evolving scripts.
Operational Evolution: Future-Proofing through Multi-Layered Verification
Security experts concluded that the most effective path forward involved a total departure from traditional, siloed defensive strategies. Analysts observed that the organizations that successfully mitigated the risks of generative exploitation were those that had implemented redundant verification protocols, ensuring that no single point of failure—technical or human—could lead to a catastrophic compromise. These leaders found that by maintaining a “Human-in-the-Loop” architecture, they could effectively catch the hallucinations and errors that even the most advanced AI models sometimes produced. This strategy allowed them to leverage the speed of automation while retaining the nuanced judgment of experienced professionals, creating a hybrid defense that was significantly more robust than either could achieve alone.
Looking back on the progress made through the current cycle, it became clear that the integration of cryptographically secure identity protocols and the use of out-of-band communication channels were the most critical steps in neutralizing the threat of deepfakes. These measures ensured that even if an attacker successfully cloned a voice or face, they could not bypass the secondary layers of authentication required for high-risk transactions. Organizations also focused on the long-term monitoring of their AI assets, treating them as a core part of the supply chain that required constant auditing and validation. By fostering a culture of continuous learning and technical agility, these firms successfully navigated the transition into an automated world. They developed “immune system” models that could detect unauthorized AI activity in real-time, effectively turning the defensive shield into an active, self-correcting mechanism. This evolution provided the necessary foundation for a secure digital future, proving that while AI can be a formidable sword, it can also be forged into an impenetrable shield for those who are prepared to adapt.