

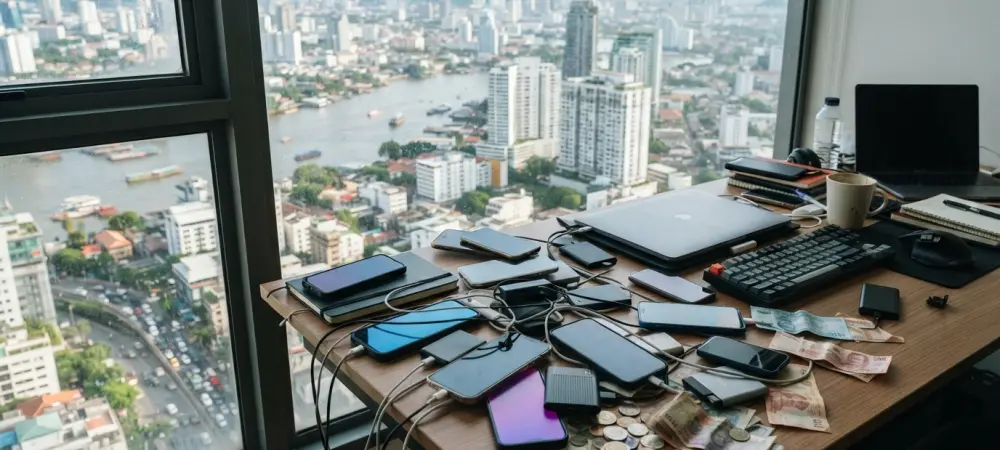
Law enforcement officials discovered that the group maintained strict operational security by recruiting members via Telegram and frequently relocating across Southeast Asian borders. The Seoul Songpa Police Station led an exhaustive investigation into this Bangkok-based syndicate, which specialized in luring victims through fraudulent sex-trade and dating-match websites. By posing as intermediaries for paid sexual encounters, the group defrauded individuals of approximately 500 million won in confirmed losses. However, police estimates based on comprehensive account analysis suggest the total scale of the scam likely reached 1.77 billion won, which is approximately $1.2 million. This operation was not merely a random act of cybercrime but a meticulously structured organization that treated digital extortion with the precision of a legitimate enterprise. The group exploited the anonymity of the digital landscape to target vulnerable individuals, using a combination of technical savvy and psychological manipulation to ensure a steady flow of illicit revenue from their victims.
Architectural Precision in Digital Crime
The Anatomy of a High-Tech Command Center
The operational structure of the phishing ring was defined by a clear hierarchy that ensured maximum efficiency and security. Members occupied a leased four-story villa in Bangkok that served as both a residence and a high-tech command center, allowing them to operate around the clock without attracting outside attention. The leadership consisted of a ringleader, general managers, team leaders, and call agents, many of whom were recruited through popular digital platforms like Google and Telegram.
To maintain operational security, every member utilized aliases and followed strict protocols regarding their physical location. The group frequently relocated their base of operations across Cambodia, Vietnam, and Thailand to stay one step ahead of local law enforcement agencies. This nomadic strategy allowed them to exploit different jurisdictional weaknesses while maintaining a centralized command structure that could quickly adapt to changing circumstances or increased police activity in a specific region, making them an elusive target for international investigators.
The Mechanics of Psychological and Financial Extortion
The syndicate’s primary tactic involved a psychological foot-in-the-door strategy that began with a deceptive low-stakes commitment. They initially requested a nominal membership fee of only 20,000 won to gain the victim’s trust and commitment. Once a victim was engaged, the group rapidly escalated their demands by citing various fabricated reasons for additional payments, such as reservation deposits, security verification charges, and system recovery costs to fix supposed technical errors on their fraudulent platforms.
In one extreme instance, a single victim was coerced into making 16 separate payments, resulting in a total loss of over 150 million won. To evade tracking, the syndicate rotated through 19 bank accounts every two weeks and even returned small portions of stolen funds to prevent victims from reporting the fraud. This calculated move provided a false sense of resolution or hope that the rest of the money would be recovered, buying the group valuable time to continue their operations and move their illicit gains into safer jurisdictions.
International Cooperation and Actionable Security Steps
The eventual dismantling of the ring was the result of a coordinated international effort involving the Korean National Police, the National Intelligence Service, and Thai authorities. This collaboration led to the arrest of ten core members and the booking of fourteen additional individuals who provided illegal bank accounts. While the ringleader remained at large, the police seized 53 pieces of evidence, including mobile phones and SSDs, which provided essential data for identifying further leads in the pursuit of the remaining fugitives.
Authorities successfully disrupted the syndicate by identifying the specific patterns of account rotation and refund baiting used to mask criminal activities. Financial institutions were encouraged to implement more robust real-time monitoring of suspicious transfers that matched these predatory profiles. Public awareness campaigns shifted toward educating individuals on identifying the psychological triggers used in phishing, specifically warning that any online request for membership fees or commissions in these contexts served as a definitive red flag for potential financial ruin.