

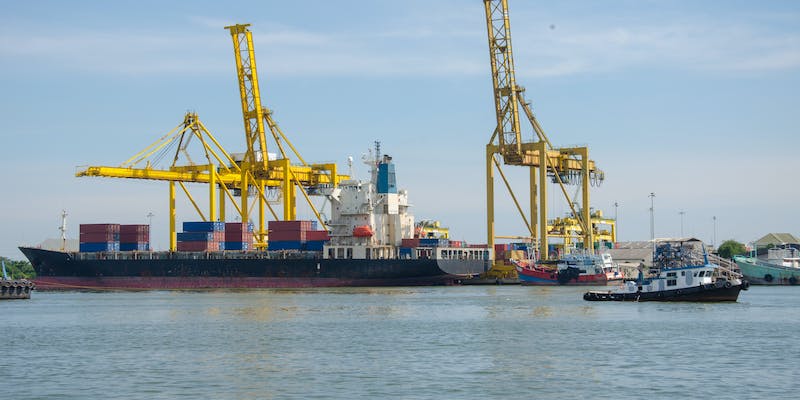
In a major cyber incident that unfolded at four major Australian ports, hackers not only incapacitated the operations but also managed to steal employee data, according to the port operator. The incident came to light on November 10 and involved the Down Under subsidiary of stevedore DP World.
Employee Data Breach by Hackers
The ramifications of the cyber incident became evident as it was revealed that the hackers had gained access to personal information belonging to both current and former employees. However, it is important to note that the hackers did not manage to obtain any customer information, which provides some level of relief amid the growing concerns of data breaches.
No ransomware malware was found, and no ransom demand has been received
In a statement, DP World clarified that its investigation had not unearthed any traces of ransomware malware on its network. Additionally, the company confirmed that it had not received any ransom demand from the hackers, which further perplexed the motive behind the cyberattack.
Impact on Operations and Logistics Systems
As a result of the incident, DP World was forced to disconnect its logistics system, leading to a backlog of approximately 30,000 shipping containers at the ports of Brisbane, Sydney, Melbourne, and Fremantle. This disruption caused significant delays and challenges in the shipping and maritime industry, raising concerns for businesses relying on timely delivery and exports.
DP World’s significance in Australian container cargo handling
DP World Australia plays a crucial role in handling Australia’s international container cargo, accounting for about 40% of the total volume each year. While the incident had a severe impact on the affected ports, operations outside Australia remained unaffected, providing some solace to global trade partners and neighboring nations.
Government response and attention to the incident
The magnitude of the cyber incident caught the attention of Australian authorities, who promptly classified it as “nationally significant.” In response, the government mobilized its resources to address the situation and mitigate any further damage. The incident served as a wake-up call for the country, highlighting the urgent need for robust cybersecurity measures.
Increase in Cyber Attacks and Data Breaches in Australia
Over the past 18 months, Australia has witnessed a surge in opportunistic ransomware attacks and data breaches, which have raised concerns within both the public and private sectors. The frequency and scale of these cyber threats have driven the government and businesses to reassess their cybersecurity strategies.
Government’s commitment to enhancing cybersecurity
In a bid to combat the growing threat landscape, Prime Minister Anthony Albanese’s administration has pledged to invest AU$587 million towards transforming Australia into a “world leader in cybersecurity” by the end of the decade. This significant investment reflects the government’s commitment to bolstering the nation’s cybersecurity infrastructure and protecting critical systems and data.
The cyber incident at Australian ports serves as a stark reminder of the ever-present and evolving threat of cyber attacks. The compromise of employee data raises concerns about identity theft, privacy, and the potential misuse of personal information. While the immediate impact was felt in the maritime industry, the incident serves as a broader call-to-action for all sectors to prioritize cybersecurity.
Moving forward, it is imperative for both the public and private sectors to continuously strengthen their cybersecurity measures, enhance threat intelligence sharing, and invest in advanced technologies. Additionally, raising awareness among employees about phishing attempts, password security, and other best practices is crucial in building a cyber-resilient workforce. Only through a collective effort can Australia protect its critical infrastructure, businesses, and citizens from the growing cyber threats in the digital age.