

Existing prohibitions against electronic surveillance in restrooms and locker rooms remain unchanged under the new legislative framework passed in Connecticut. The signing of Public Act No. 26-73 by Governor Ned Lamont signals a transformative shift in the relationship between employers and staff members across the state. This legislation addresses the rapid integration of intrusive technologies like smart glasses and biometric scanners into daily operations. While the convenience of these tools for productivity tracking is undeniable, the legal landscape now mandates a level of transparency that was previously discretionary for most private enterprises. By requiring clear disclosure, the state aims to mitigate the psychological stress and potential overreach associated with invisible monitoring systems. This mandate ensures that every individual entering a professional environment understands the digital footprint they leave behind. The focus shifts from clandestine observation to a regulated agreement where tracking serves specific goals.
Establishing Standards: The Requirements for Workplace Transparency
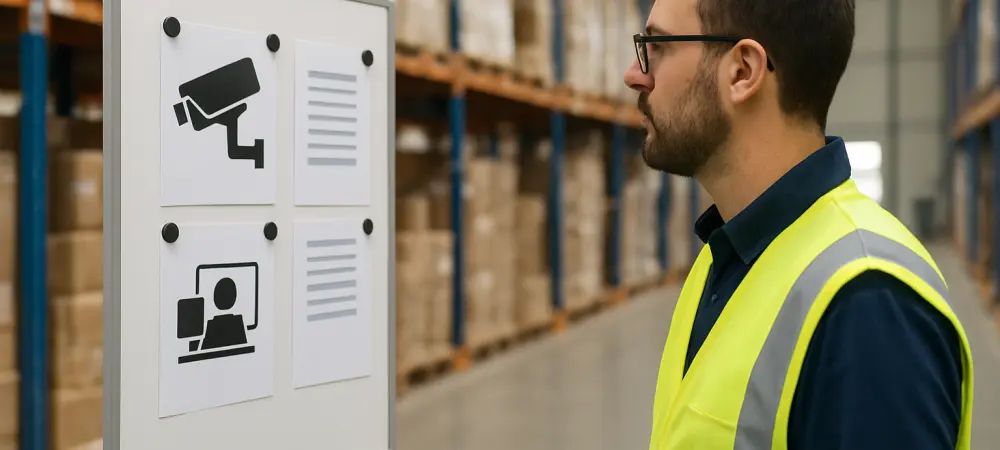
Employers must now navigate a rigorous set of requirements that prioritize the right to be informed about how performance data is collected. Starting this October, written notification is no longer an optional best practice but a legal prerequisite for any form of electronic oversight. This includes traditional methods like video surveillance in retail zones and sophisticated digital tools such as keystroke logging and GPS tracking in commercial vehicle fleets. The law specifies that notice must be placed prominently within the physical work environment, ensuring it remains visible to both current personnel and prospective hires. For those joining an organization after the effective date, the onboarding process must include a comprehensive statement detailing which behaviors are subject to monitoring and the potential triggers for increased scrutiny. This systematic approach aims to remove any ambiguity regarding corporate expectations and the extent of digital recording, creating a standardized protocol for transparency that bridges the gap between management.
Industry Impact: Addressing Modern Surveillance Technologies
The breadth of this legislation encompasses various industries, from manufacturing floors where automated systems track efficiency to high-tech offices utilizing sophisticated software for remote management. By requiring employers to identify the specific locations of surveillance, the law prevents the broad, unspecified monitoring that has often led to privacy disputes in the past. This clarity is particularly vital in the logistics sector, where the use of telematics and interior vehicle cameras has become standard. Companies are now tasked with justifying the necessity of these measures while explicitly informing drivers of when their actions are being recorded. Furthermore, the inclusion of biometric data under this framework reflects a growing concern over the collection of unique physiological markers. This requirement compels organizations to evaluate their data retention policies and ensure that the collection of such sensitive information is strictly aligned with the disclosed operational needs. The era of set and forget surveillance is over.
Balancing Security: Navigating Investigative Exemptions and Liability
Despite the heavy emphasis on transparency, the legislative framework acknowledges that there are scenarios where immediate, unannounced monitoring is essential for safety and legal protection. Employers retain the authority to bypass notice requirements when there is a reasonable suspicion of illegal activity or a violation of internal rights, such as the creation of a hostile work environment. This provision ensures that management can effectively respond to threats or internal misconduct without alerting the perpetrator and compromising the integrity of an investigation. Information gathered through these lawful, targeted actions remains admissible in disciplinary proceedings or criminal prosecutions, maintaining the balance between individual privacy and collective security. However, this exception is not a loophole for general surveillance; it requires a documented justification that links the monitoring to a specific, credible concern. This nuance forces legal teams to be more deliberate.
Proactive Compliance: Implementing New Internal Privacy Policies
To navigate this evolving regulatory environment, businesses proactively updated their internal handbooks and revised their onboarding materials to align with the new standards. Legal experts advised that supervisors underwent specialized training to handle surveillance data with heightened ethical considerations, ensuring that all monitoring remained within the bounds of state and federal privacy regulations. The implementation of a tiered penalty system, which started at five hundred dollars and rose to three thousand dollars for repeated violations, served as a strong incentive for meticulous compliance. Organizations that integrated these changes early found that fostering a culture of transparency actually improved employee morale and reduced the friction often caused by perceived privacy invasions. These entities moved beyond mere adherence to the law by establishing clear channels for feedback regarding monitoring practices, which helped in refining operational efficiency without sacrificing trust.